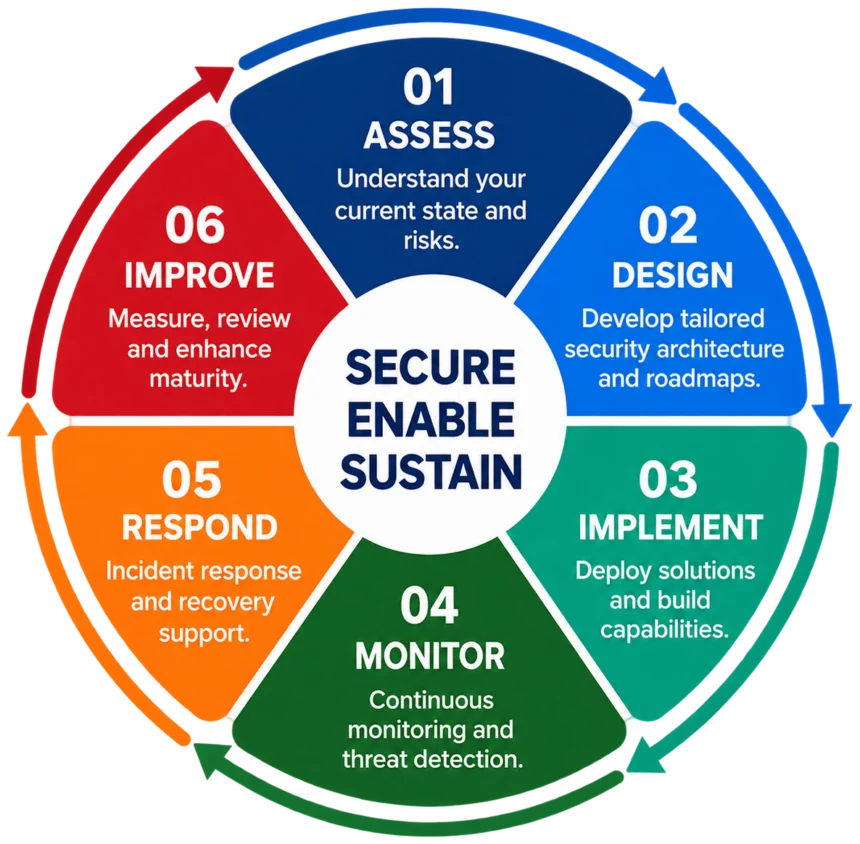
ISDT designs and implements risk-based Information Security Management Systems, including context assessment, asset and risk management, risk treatment, Statement of Applicability, security policies, controls, internal audit and certification readiness.
What We Do
- ISMS scope
- Information-security risk assessment
- Asset management
- Risk treatment
- Statement of Applicability
- Policies and controls
- Internal audit
- Management review
- Certification readiness
ISMS & ISO/IEC 27001
Design and implementation of risk-based Information Security Management Systems through to certification readiness.
Learn more ↗