ISDT / Governance, Risk & Compliance

GRC & Regulatory
Compliance

One Governance Framework. One Risk View. Continuous Compliance Across the Organization.

TRUSTEDOPERATIONS
SUSTAINABLEGROWTH
STRONGER STAKEHOLDERCONFIDENCE

What We Offer

GRC Services

End-to-end governance, risk and compliance services tailored to your organization, from framework design to independent assurance.

01 / SERVICE

Governance Advisory

Governance frameworks, board and committee structures, policies and decision-making models aligned with strategy.

Learn more ↗
02 / SERVICE

Enterprise Risk Management (ERM)

Enterprise risk frameworks, risk assessments, registers and treatment plans aligned with ISO 31000 and COSO ERM.

Learn more ↗
03 / SERVICE

Regulatory Compliance

Compliance with local, regional and international legal, regulatory and contractual requirements.

Learn more ↗
04 / SERVICE

Management Systems Integration

One governance architecture integrating ISO management systems, GRC processes and regulatory requirements.

Learn more ↗
05 / SERVICE

Policies, Procedures & Controls

Policies, SOPs and controls that turn governance and compliance requirements into day-to-day practice.

Learn more ↗
06 / SERVICE

Internal Controls

Design, mapping and effectiveness testing of business, operational, financial, technology and compliance controls.

Learn more ↗
07 / SERVICE

Internal Audit & Assurance

Independent internal audits, compliance reviews and maturity assessments that deliver evidence-based assurance.

Learn more ↗

Integrated compliance architecture

Standards, frameworks & alignment

We translate global best practice and regional obligations into a GRC system built for your sector.

ISO Standards (Governance, Risk & Compliance)

ISO9001Quality Management
ISO14001Environmental Management
ISO45001Occupational Health & Safety
ISO/IEC27001Information Security
ISO22301Business Continuity
ISO/IEC20000-1IT Service Management
ISO27701Privacy Information Management
ISO31000Risk Management
ISO37001Anti-Bribery Management
ISO37301Compliance Management
ISO37000Governance of Organizations
Other
ISO Standards
Sector Specific
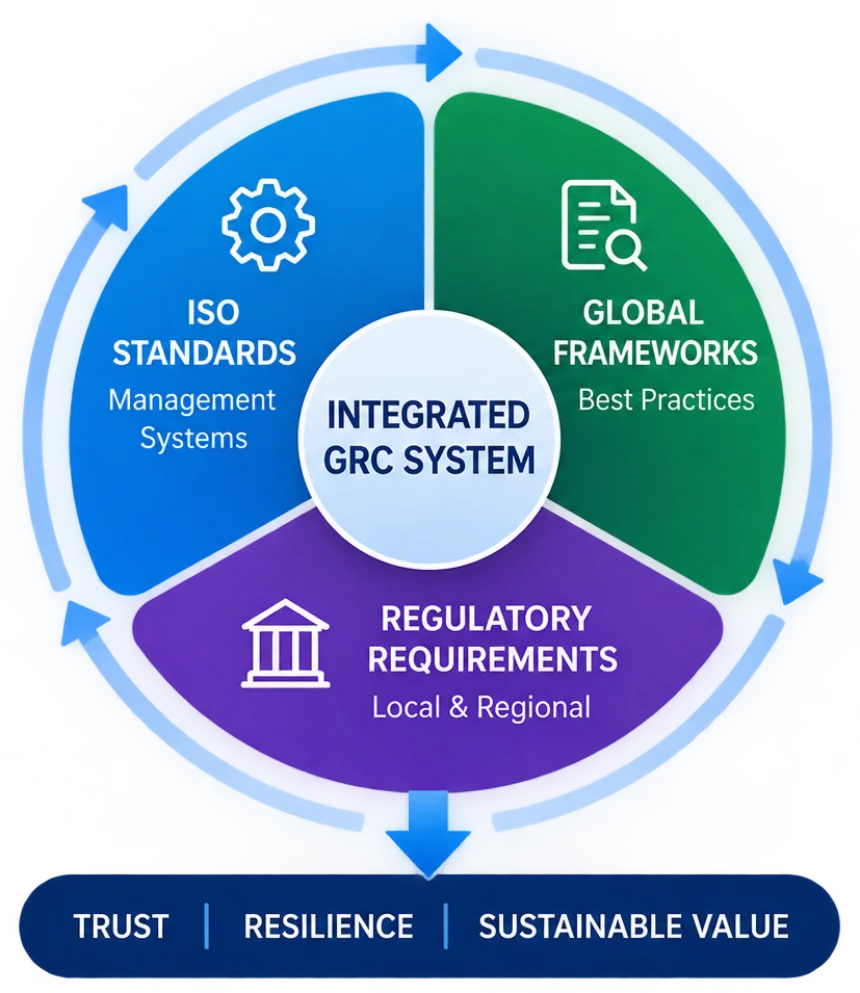
Integrated GRC System: ISO standards, global frameworks and regulatory requirements combined for trust, resilience and sustainable value

Global Frameworks & Best Practices

NISTCSF 2.0Cybersecurity
COBIT2019IT Governance
COSOERMEnterprise Risk Management
PCI DSSPayment Card Industry
SCFSecurity Controls Framework
NFPAFire & Life Safety (Selected Sectors)
GDPRData Protection & Privacy
GRISustainability Reporting

Regional Regulatory Requirements

NCA / NCSACybersecurity (KSA)
SDAIAData & AI (KSA)
SAMA(Where Applicable) (KSA)
ZATCATax & Compliance (KSA)
JordanianRegulations
UAERegulatory Requirements
Other RegionalRegulators (Qatar, Bahrain, Oman, etc.)

How We Deliver

Our Approach

A structured path from assessment to continuous improvement, built around your organization’s context.

01

Govern

Set strategy, policies, objectives and accountability across the organization.

View Details +
02

Identify

Map processes, stakeholders, obligations, standards and risks.

View Details +
03

Assess

Assess enterprise, HSE, cyber, environmental and compliance risk.

View Details +
04

Control

Design and deploy policies, procedures and technical controls.

View Details +
05

Comply

Align with ISO standards, laws, regulations and industry frameworks.

View Details +
06

Assure

Monitor performance through KPIs, audits and management review.

View Details +
07

Improve

Drive corrective action, lessons learned and continual improvement.

View Details +

Start a conversation

Transform Fragmented Management Systems into
Integrated Enterprise Governance.

Partner with ISDT Consultants to design and implement a GRC framework that creates long-term value and a safer, more resilient tomorrow.

PEOPLESAFER OPERATIONSBUSINESSSTRONGER ORGANIZATIONSSOCIETYA MORE RESILIENT TOMORROW
error:
Scroll to Top